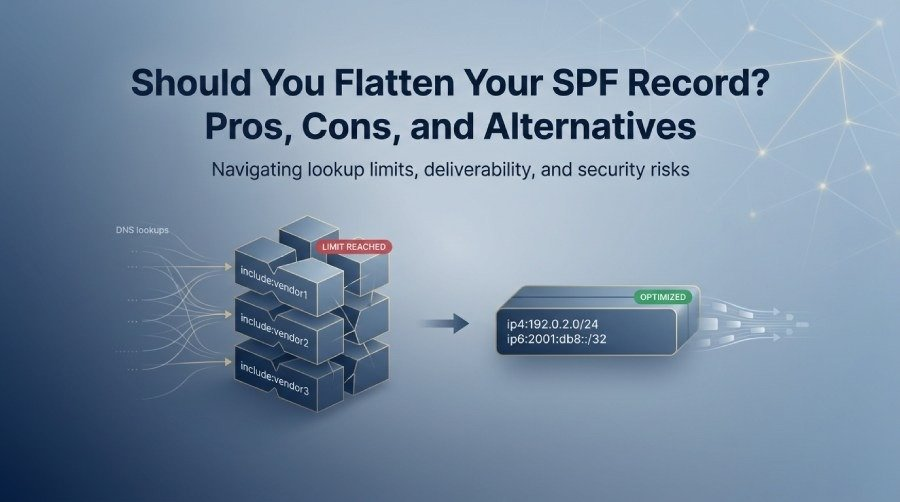
SPF flattening is the practice of replacing SPF include references with the actual IP ranges those includes resolve to. Instead of publishing an SPF record filled with entries such as include:_spf.google.com, include:sendgrid.net, or an include: statement from an email vendor, you publish a flat SPF record containing authorized IP addresses directly.
This is usually done to avoid the SPF lookup limit defined in RFC 7208. SPF allows a maximum of 10 DNS-querying mechanisms during authentication checks. These include the SPF include mechanism, a, mx, ptr, exists, and redirect. If your SPF configuration exceeds that limit, the receiving Mail server may return a PermError, causing SPF pass/fail results to become unreliable and potentially hurting deliverability.
Organizations often hit the SPF lookup limit when they use multiple third-party email senders, such as Google Workspace, Microsoft 365, SendGrid, Mailchimp, Mandrill, Zoho, Amazon SES, and Outlook.com. Each email vendor, marketing platform, CRM tool, or cloud services provider may add its own include mechanism, and each nested include can trigger additional DNS lookup activity.
How SPF flattening turns includes into IP ranges
A typical SPF record might contain several includes:
v=spf1 include:_spf.google.com include:sendgrid.net include:mail.zendesk.com -all
With SPF flattening, those includes are resolved into IP ranges, producing a flat SPF record. A flattened record may contain ip4 and ip6 mechanisms instead of vendor-managed includes. This reduces DNS lookups because IP mechanisms do not trigger a DNS lookup.
However, a flat SPF record is often a static SPF record. That means it will not automatically reflect IP address changes made by email vendors unless it is updated. This is where the difference between manual SPF flattening and dynamic SPF flattening becomes important.
Manual SPF flattening vs dynamic SPF flattening
Manual SPF flattening involves using an SPF checker, command-line DNS tools, or PowerDMARC’s SPF Flattening Tool to resolve every include mechanism and nested include, then publishing the resulting IP ranges at your DNS registrar. It can work, but manual SPF flattening creates ongoing SPF record maintenance because vendor IP ranges can change without notice.
Dynamic SPF flattening uses an SPF flattener or hosted SPF provider to keep the flattened record updated. A dynamic SPF flattening service can monitor vendor IPs, refresh IP ranges, and provide automatic updates when third-party vendors change their infrastructure. PowerDMARC, PowerSPF, and other hosted SPF solution providers offer this type of SPF flattener functionality to reduce maintenance burden and prevent stale records.
The Main Benefits: Avoiding DNS Lookup Limits and Improving Deliverability
Staying under the SPF lookup limit
The SPF lookup limit is one of the most common causes of SPF failure in modern domain authentication. A company may start with Google Workspace or Microsoft 365, then add SendGrid for transactional mail, Mailchimp for campaigns, Salesforce for CRM alerts, Zendesk for support, and Amazon SES for applications. Each service may introduce an include mechanism, and each nested include can add more DNS lookups.
SPF flattening reduces the number of live DNS lookup operations required during authentication checks. A flat SPF record replaces vendor includes with IP ranges, so the receiving Mail server does not need to chase multiple SPF sub-records. This can prevent PermError, reduce silent SPF failures, and improve SPF pass/fail consistency.
An SPF flattener can also identify unnecessary includes, duplicate IP ranges, and sources that no longer send mail for your domain. That makes SPF flattening useful not only for limit management but also as part of a broader SPF audit or SPF record audit.
Deliverability and authentication stability
SPF is only one part of email authentication, alongside DKIM and DMARC, but a broken SPF configuration can still affect deliverability. If authentication checks fail because of excessive DNS lookups, recipients may treat messages with suspicion—especially when your DMARC policy is set to quarantine or reject.
A properly managed flat SPF record can reduce authentication uncertainty. It helps receiving systems validate approved senders faster and more consistently. This is especially useful for high-volume senders using cloud services, marketing platforms, or CRM tools where domain authentication must remain stable.
That said, SPF flattening is not a deliverability cure-all. DKIM alignment, DMARC reports, Bounce processing, domain reputation, and content quality still matter. SPF reporting through DMARC reports can help you confirm whether SPF flattening is improving authentication outcomes or simply masking a deeper SPF configuration problem.
The Risks and Drawbacks: Maintenance Burden, Stale IPs, and Security Gaps
Static records, stale IPs, and vendor changes
A static SPF record created through manual SPF flattening can become outdated quickly. Email vendors and cloud services frequently change IP ranges as they scale infrastructure. If your flat SPF record does not reflect those IP address changes, legitimate mail may fail SPF.
This is the core drawback of manual SPF flattening: you must monitor vendor IPs continuously. If SendGrid, Mailchimp, Amazon SES, Microsoft 365, or another provider updates its SPF include mechanism, your static SPF record will not inherit that update. The result can be validation failures, silent SPF failures, or unexpected deliverability problems.
Dynamic SPF flattening reduces this risk by updating the flattened record automatically. A good SPF flattener checks vendor includes on a schedule, detects IP address changes, and pushes automatic updates. Still, dynamic SPF flattening depends on the reliability of the hosted SPF provider, so you should evaluate uptime, audit logs, and failover behavior.

Record size, DNS limits, and security risks
A flat SPF record can become very large. When many IP ranges are expanded from several nested include chains, record bloat can push you toward the DNS TXT record size limit. SPF records that are too large may require SPF folding across multiple quoted strings in DNS, and improper SPF folding can cause parsing errors.
Excessive flattening can also create security risks. If old IP ranges remain authorized after an email vendor stops using them, unauthorized systems may still pass SPF. This is particularly dangerous when combined with weak DKIM practices or an overly permissive DMARC policy.
For this reason, SPF compression and careful optimization matter. An optimized include, hosted SPF, or dynamic SPF flattening setup can keep the record smaller and fresher than manual SPF flattening. Some systems use SPF Macros or SPF macros for advanced routing, though these should be implemented carefully because they can increase complexity and must remain compliant with authentication standards.
When SPF Flattening Makes Sense—and When It Doesn’t
SPF flattening makes sense when your domain genuinely exceeds or is close to the SPF lookup limit and you rely on several third-party email senders. It is also useful when your SPF audit shows multiple nested include chains that create unnecessary DNS lookup overhead.
Good candidates for SPF flattening
SPF flattening is usually appropriate when:
- Your SPF checker shows more than 10 DNS lookups.
- You receive PermError results in DMARC reports.
- You use many email vendors, cloud services, marketing platforms, or CRM tools.
- Your SPF configuration contains several nested include references.
- You need stable authentication checks for high-volume sending.
However, SPF flattening is less appropriate for simple environments. If your domain only uses Google Workspace or Microsoft 365 and has one clean include mechanism, a flat SPF record may add unnecessary maintenance burden. Likewise, if your email vendor changes IP ranges frequently, manual SPF flattening can become risky unless you have a strict SPF record maintenance process.
Dynamic SPF flattening is generally safer than manual SPF flattening for complex senders. A managed SPF flattener can maintain a static-looking record while updating the underlying IP ranges. But even dynamic SPF flattening should be paired with regular SPF record audit activity, DMARC monitoring, and DKIM alignment checks.

Better Alternatives and Best Practices for Managing SPF Records
Use hosted SPF, audits, and optimized includes
A hosted SPF provider can help you stay below the SPF lookup limit without relying entirely on manual SPF flattening. Hosted SPF centralizes SPF record maintenance, supports automatic updates, and can provide an optimized include that represents multiple approved senders. This approach is often cleaner than publishing a large flat SPF record directly at your DNS registrar.
Best practices include:
- Run an SPF checker regularly to identify DNS lookups, nested include chains, and PermError risks.
- Perform an SPF audit whenever you add or remove third-party vendors.
- Remove unused email vendor includes from your SPF configuration.
- Prefer DKIM and DMARC alignment for services that support strong domain authentication.
- Use dynamic SPF flattening instead of manual SPF flattening when vendor IP address changes are frequent.
- Monitor DMARC reports for SPF pass/fail trends, Bounce patterns, and unauthorized sources.
- Avoid excessive record bloat that could exceed the DNS TXT record size limit.
- Consider SPF compression, SPF sub-records, or a hosted SPF solution when managing many IP ranges.
SPF Flattening Tool can simplify this process by combining SPF checker capabilities, hosted SPF, dynamic SPF flattening, and reporting. The goal is not merely to create a flattened record, but to maintain a secure, accurate, and resilient email authentication system.


